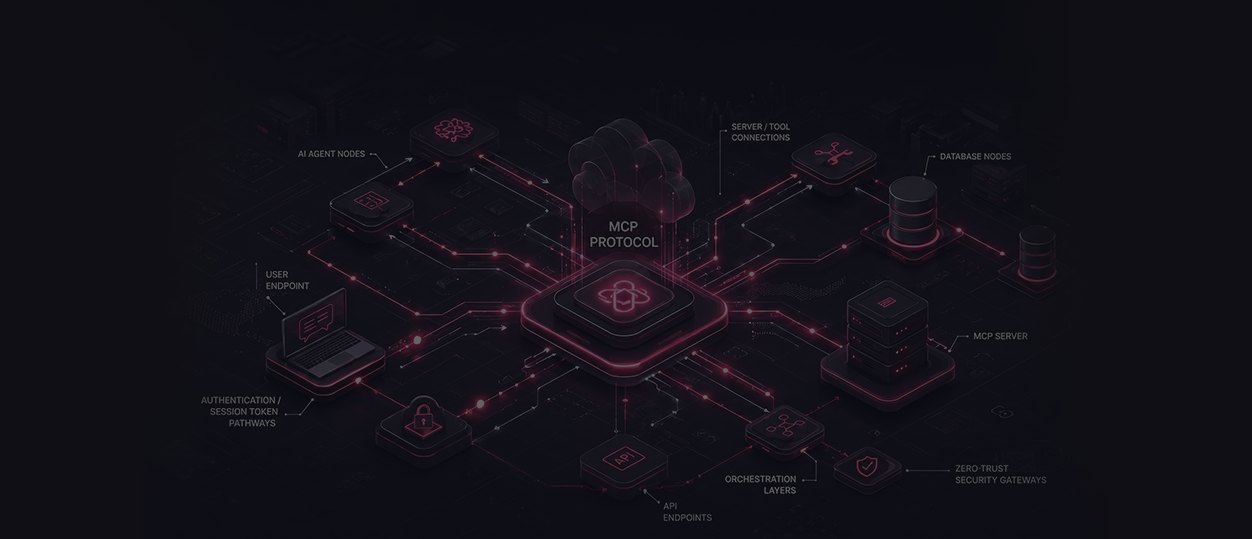
01
Endpoint Outside the Zone
The request starts at the edge
AI agent requests originate from user endpoints that may operate outside the security boundaries protecting critical enterprise systems.

X-PHY AI ARMOR
X-PHY AI Armor protects the endpoint where every AI agent request begins and helps safeguard the enterprise resources connected through MCP servers.
Combining X-PHY Cybersecure SSD, AI Armor Agent and AI Armor Platform, it brings hardware rooted trust, authenticated integration, security policies and rules into the AI workflow.
X-PHY Cybersecure SSD · AI Armor Agent · AI Armor Platform · Hardware Root of Trust
THE ENDPOINT TRUST GAP
AI agents connect users to sensitive business systems and enterprise data. However, authenticated sessions alone cannot guarantee endpoint security. A compromised device may expose trusted access to attackers, putting connected resources at risk.
X-PHY AI Armor helps close this gap by verifying trust at the hardware level, not just at login.
The request starts at the edge
AI agent requests originate from user endpoints that may operate outside the security boundaries protecting critical enterprise systems.
Authentication backed by hardware trust
Session tokens establish authenticated access, while X-PHY Hardware Root of Trust provides an additional hardware backed foundation for endpoint trust.
One connection can reach multiple systems
Agent Servers and connection services route AI requests to enterprise resources, making the trust and security of each connected endpoint essential.
Protection must extend beyond the endpoint
The systems an AI agent can reach, not the device itself, are the real targets behind every request.
X-PHY PROTECTION STACK
Hardware security at the endpoint
Establishes a hardware rooted security foundation within endpoint storage, helping protect against compromise and unauthorized activity.
Connects hardware security to the platform
Communicates SSD status and security events to the AI Armor Platform and executes supported security response commands.
One authenticated integration point
Provides an authenticated interface for endpoint communication, security event collection and integration with AI agent workflows.
Hardware backed command authentication
Uses API key authentication together with the SSD's unique secret key and a one time password model to verify supported security commands.
Centralized security response
Coordinates Lock, Wipe and status query commands for enrolled endpoints through the AI Armor Platform.
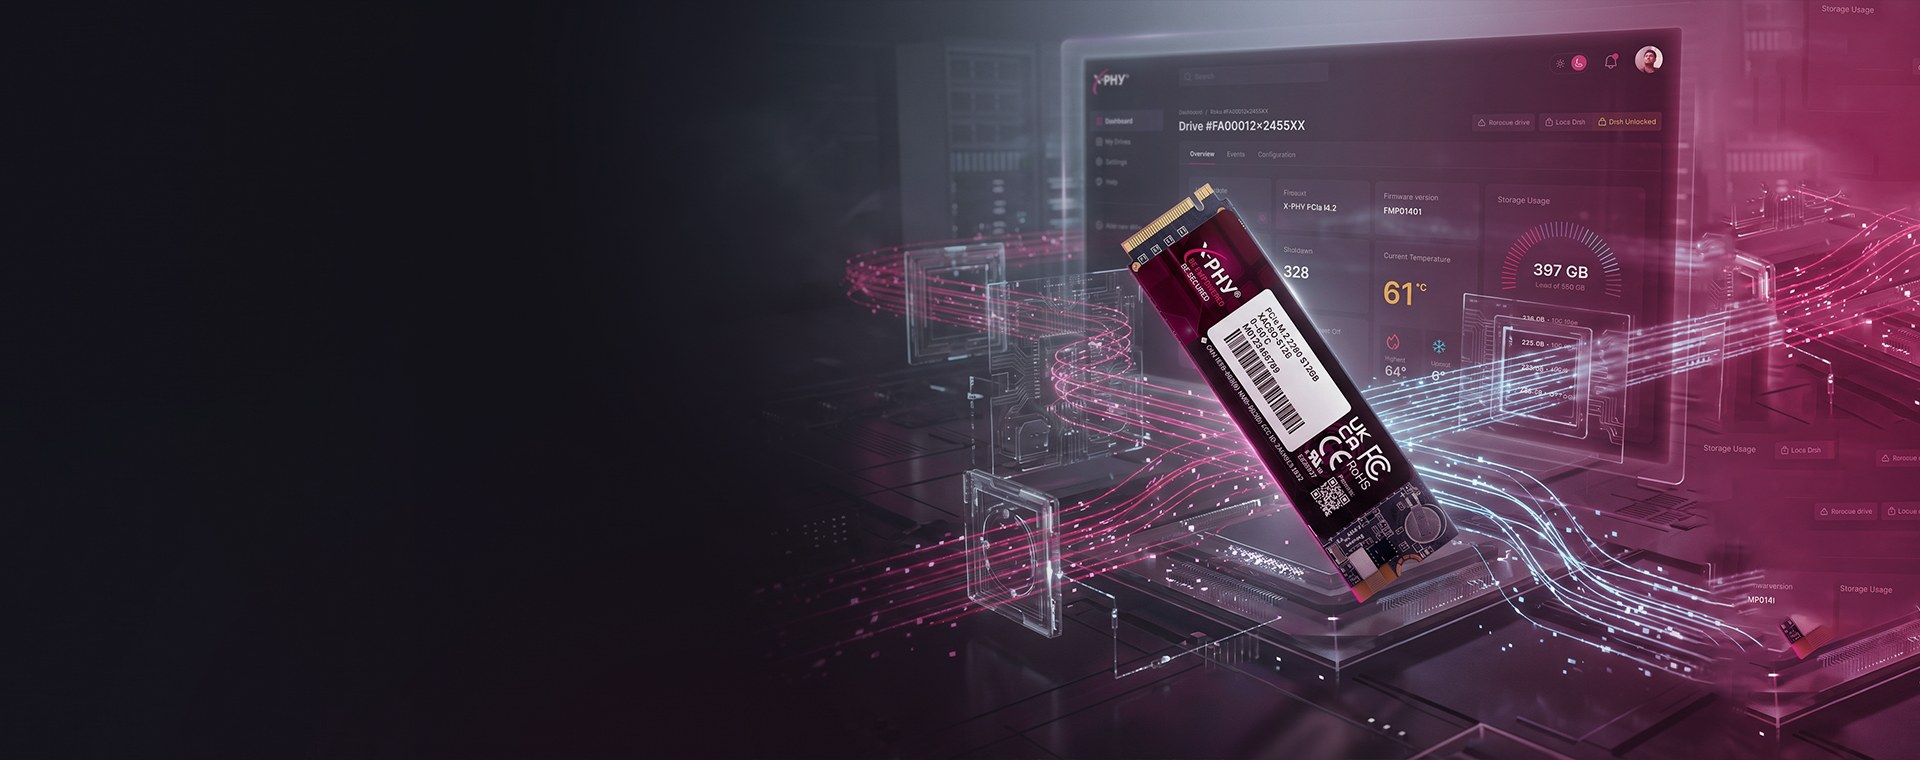
PROTECTION & INTEGRATION
X-PHY AI Armor combines autonomous hardware security with authenticated platform integration.
Firmware protection and embedded hardware sensors operate independently at the endpoint, while the AI Armor Platform connects endpoint security events and response capabilities to the wider AI agent workflow.
AI AGENT ARCHITECTURE
AI agent workflows rely on authenticated sessions and connection services to reach enterprise systems. The MCP Server is the common link to those resources, while AI Armor adds hardware rooted security around the workflow.
CONNECTED RESOURCES
RESULT RETURNS ← MCP SERVER ← AGENT SERVER ← ENDPOINT
A user or application initiates an AI agent request from the endpoint.
The Agent Server authenticates the session before processing the request.
The AI workflow passes the request toward the appropriate MCP Server.
The MCP Server connects the request to the relevant database, AI model, business tool or service.
The result travels back through the AI workflow to the requesting endpoint.
BEYOND ENDPOINT PROTECTION
Everything an AI agent can reach through an MCP server becomes part of the AI ecosystem, and part of its attack surface.
X-PHY AI Armor extends protection to these connected resources by combining three security elements into one foundation.
The result is stronger trust in every interaction between endpoints, AI agents and enterprise systems.
X-PHY AI ARMOR SECURITY FOUNDATION
Trust Begins in Hardware
The Cybersecure SSD gives each endpoint a hardware backed starting point for trusted authentication across AI connected environments.
Protection Guided by Defined Policies
Policies establish requirements for trusted operations and help align AI agent interactions with enterprise security expectations.
Consistent Security Decisions
Security rules help guide the handling of security events and supported responses, strengthening protection across connected AI workflows.
WHAT THE FOUNDATION HELPS PROTECT
Records that AI agents query on a user's behalf
The models and inference services your agents rely on
Applications agents can act through, not just read from
Intellectual property and sensitive information across the business
From the SSD at the endpoint to the resources behind the MCP Server, AI Armor helps build trust into each step of the AI workflow.
WHEN TRUST IS HIJACKED
The workflow itself does not change. When attackers gain control of an authenticated session, they may misuse the trusted AI workflow to reach connected business systems.
WHAT AN ATTACKER MAY ATTEMPT
SAME ROUTE · SAME SESSION · DIFFERENT OPERATOR
The attack begins at the device
Malware, phishing or stolen credentials may give attackers access to an endpoint.
Attackers inherit trusted access
A compromised session may allow unauthorized activity under legitimate user permissions.
Malicious requests follow legitimate paths
Attackers may attempt to use existing AI connections to reach internal resources.
Exposure spreads across connected systems
Every system connected to the compromised workflow may face increased security risk.
One compromised endpoint can expose multiple connected resources, making hardware rooted protection and policy driven security essential.
BUILT INTO THE ENDPOINT
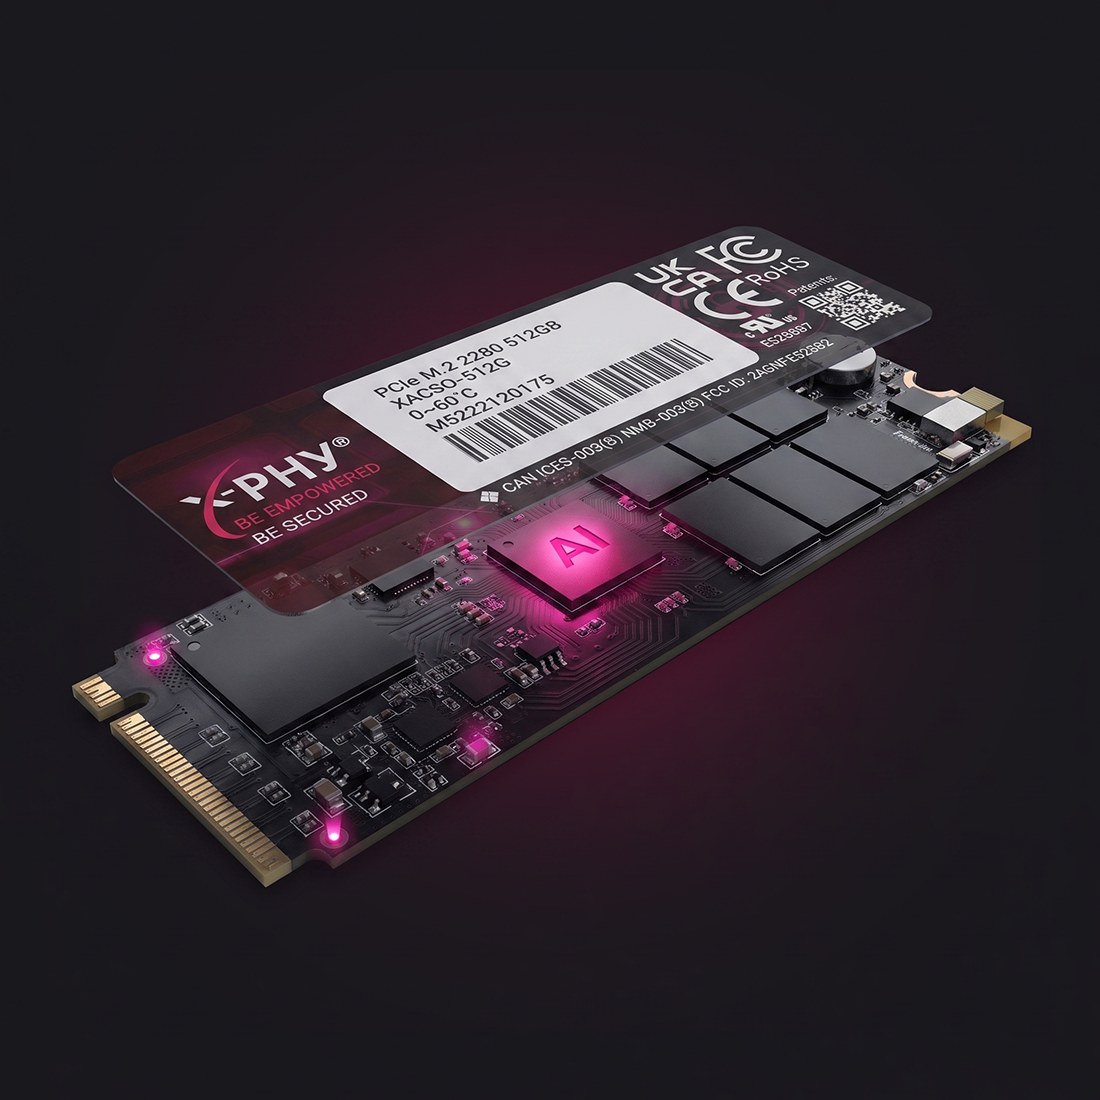
AI One Core monitors storage activity at firmware level to identify suspicious behavior and potential threats, including previously unknown attack patterns.
Hardware based encryption protects data stored on the X-PHY Cybersecure SSD.
Built in sensors support physical tamper detection and security monitoring independently of installed software or network connectivity.
Supports automatic security lockdown behavior when configured drive removal conditions are detected.
CLEAR ANSWERS. ZERO CONFUSION.
It is X-PHY's security solution for AI agent workflows, built on three parts: the Cybersecure SSD inside the endpoint, the AI Armor Agent running on the device and the AI Armor Platform for central management.
Everything AI agents reach through MCP servers, from company data and AI models to the business tools and assets behind them.
Session credentials can be stolen from a compromised device. Hardware Root of Trust adds a second anchor inside the SSD itself, which is far harder for an attacker to take over.
Hardware trust tells AI Armor whether an endpoint can be trusted. Policies and rules decide what happens next, so the same situation always gets the same response.
The MCP Server provides a standardized interface that allows AI applications and agents to interact with supported enterprise tools, data sources and services.
The Agent Server manages authenticated interactions and routes requests within the AI agent workflow.
Through the AI Armor Agent on each endpoint. The agent reports to the platform over an authenticated API and carries out the commands the platform sends back.
Each command is checked twice: against a valid API key, and against a one time password tied to that SSD's unique secret key.
Three commands for enrolled endpoints: Lock to secure the drive, Wipe to erase its data and status query to check its current state.
No. The protection runs locally on the drive, so it keeps working even when the endpoint is offline.
SECURE YOUR AI ECOSYSTEM
See how AI Armor protects the device where AI agent requests begin and strengthens trust across every system those requests reach, in a live session with the X-PHY team.
Book A Demo SessionAI Agent Security · Endpoint Protection · Device Trust
X-PHY AI Assistant
Before we start — who are we chatting with?
We use your email only to follow up on this conversation.